Telefónica Tech Cyber Security Weekly Briefing, 18 – 24 June Microsoft Office 365 and Cloudflare services went down worldwide Multiple web services were interrupted worldwide last Tuesday. The source of these incidents was Microsoft Office 365 on the one hand...
Telefónica Tech Attacking login credentials An access credential is basically a username and password associated with a person and the access permissions granted to that person for an application, service or system. An access...
Telefónica Tech Cyber Security Weekly Briefing, 13 – 17 June Hertzbleed. New side-channel attack on AMD and Intel processors Security researchers at several US universities have discovered a new side-channel attack affecting Intel and AMD processors, called Hertzbleed. What is remarkable...
Telefónica Tech Cyber Security Weekly Briefing, 6 – 10 June LockBit threatens Mandiant after linking them to Evil Corp The LockBit 2.0 ransomware group announced on its dark web publishing page afternoon, 6 May, the alleged compromise of cybersecurity firm...
Telefónica Tech Cyber Security Weekly Briefing, 28 May – 3 June Rapid evolution of the EnemyBot botnet Since its discovery last March by Securonix researchers, the botnet known as EnemyBot, focused on carrying out DDoS attacks, has continued to expand, thanks...
Telefónica Tech Cyber Security Weekly Briefing, 21–27 May Unpatched vulnerability in PayPal Security researcher H4x0r-DZ has disclosed an unpatched vulnerability in PayPal’s money transfer service that could allow attackers to trick victims into stealing money by completing targeted...
Telefónica Tech Cyber Security Weekly Briefing, 13–20 May VMware fixes critical vulnerabilities in several of its products VMware has issued a security advisory to fix a critical authentication bypass vulnerability affecting several of its products. Identified as CVE-2022-22972...
Telefónica Tech Cyber Security Weekly Briefing, 7–13 May Vulnerability in BIG-IP exploited to erase data On May 4th, F5 fixed, among others, a vulnerability affecting BIG-IP devices (CVE-2022-1388 CVSSv3 9.8), which could allow an unauthenticated attacker with network...
Telefónica Tech Cyber Security Weekly Briefing, 24 April – 6 May TLStorm 2 – Vulnerabilities in Aruba and Avaya switches Researchers at Armis have discovered five vulnerabilities in the implementation of TLS communications in multiple models of Aruba and Avaya switches....
Telefónica Tech Cyber Security Weekly Briefing 22–29 April New malicious RedLine distribution campaign Researchers at BitDefender have published a report on a new RedLine malware distribution campaign. According to the analysts, malicious actors are using the RIG Exploit...
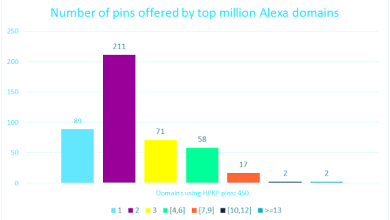
Florence Broderick New Report: Most common errors when implementing HPKP, HSTS and preload conditions We have collected and visited two different sources of domains and webpages, Alexa top million domains, and Shodan. These results come from November 2016 searches. From those domains, we...
Florence Broderick Social engineering is more active than ever The fact that Social Engineering has been the easiest method used by the scammers is not new. What we are going to describe in this blog today has been...
Florence Broderick Research: On the overexposure of Amazon credentials in mobile apps The development of mobile applications that interact with common services in mobility environments such as Amazon Simple Storage Service (S3), Amazon Simple Notification Service (SNS), Amazon Simple Queue Service...